SecurityVulnerability.io
Collect, Display, Alert.
The Cyber Security
Vulnerability Database
Trending
Vulnerabilities
If it's trending, then it's probably important.
Patch quicker!
Spoofing Vulnerability in Microsoft Office Outlook
Unauthenticated Remote Code Execution in React Server Components Framework
Use After Free Vulnerability in Google Chrome
Improper Synchronization Vulnerability in Apache HTTP Server's mod_http2
Arbitrary Code Execution Vulnerability in Confection WordPress Plugin
Authentication Bypass in SonicWall SonicOS SSLVPN Service
User Enumeration Vulnerability in OpenSSH by The OpenBSD Foundation
Authorization Bypass Vulnerability in Entra Device Registration by Microsoft
Heap-based Buffer Overflow in SQL Server by Microsoft
Latest Ransomware
Vulnerabilities
Local Privilege Escalation in Gaia OS by Check Point
CVE-2026-123039CheckpointQuantum Security Gateway💰👾🦅📰7.8HIGHUse-After-Free Vulnerability in MongoDB Server's Replication Component
CVE-2026-118383MongodbMongodb Server📈💰👾🟡📰9.5CRITICALFile Permission Vulnerability in Kiro CLI on macOS and Linux
CVE-2026-124848AmazonKiro Cli💰👾📰6.8MEDIUMiOS 17.5 and Later Fixes Bypass Pointer Authentication Vulnerability
CVE-2024-27834AppleSafari📈💰👾🦅📰5.5MEDIUMImproper Resource Isolation in Amazon EKS Network Policy Agent
CVE-2026-122266AwsAws-network-policy-agent💰👾📰6.3MEDIUM
13 November 2026
12 November 2026
6 November 2026
5 November 2026
Exploit Intelligence by SecurityVulnerability.io
Understand what's being exploited!
Mobile friendly intelligent alerting 🔔
What you need to know, when you're on the go. Easy to access information and alerts sent directly to you.
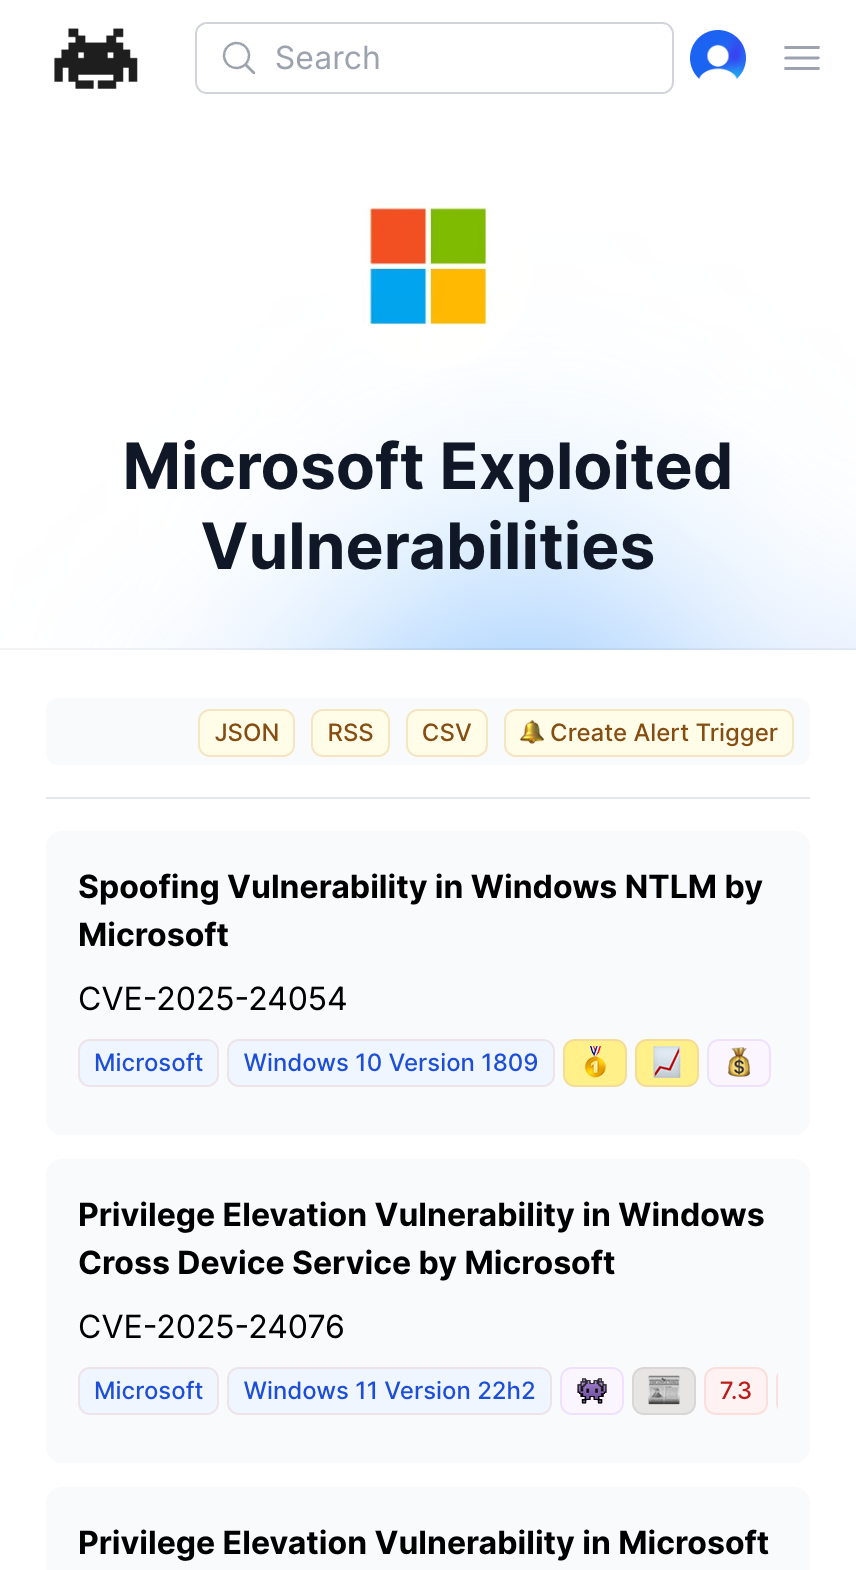
Highlighting what's important
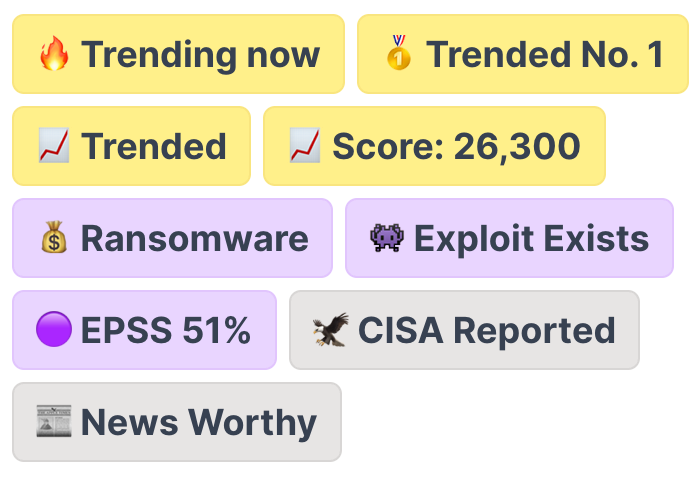
Emerging vulnerabilities & threats
Every hour we analyze over 50 data sources to identify the emerging threats that matter to you, and your business!
Powerful visuals
We believe in the power of making things simple. The site is designed to be screenshot friendly, so you can share the information with your team.
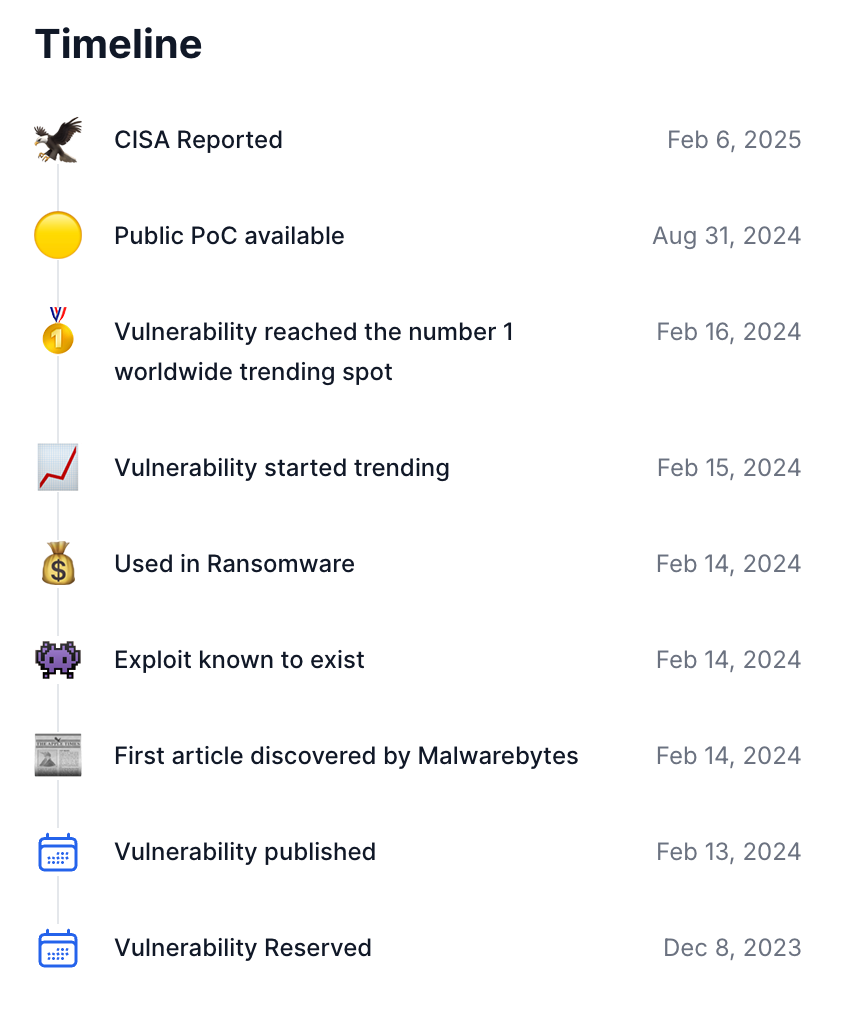
Trusted by
SecurityVulnerability.io was built to help colleagues in the industry.
- Active Users
- 30k+
- Data Sources
- 50+
- Vulnerabilies Tracked
- 200k+
- New Vulnerabilities Each Day
- 120+
5 out of 5 stars
“Understanding what's really important in a world with too much information allows Cytadel to always be at the cutting edge of protective activites.”
Boost your productivity.
Start using SecurityVulnerability.io
The database is open and free to use.
Advanced queries and alerting require a free account.
Frequently asked questions
- 🔐 What is SecurityVulnerability.io?
- SecurityVulnerability.io is a live platform that curates, summarizes, and explains critical Cyber Security vulnerabilities (CVEs) for security professionals, engineers, and IT teams. We make it easier to track threats across vendors like Microsoft, Cisco, Apple, and more — without the noise.
- 🔍 How does SecurityVulnerability.io work?
- We analyze thousands of sources, including CVE databases, vendor advisories, and security blogs, to provide you with the most relevant and actionable information. Our platform uses advanced algorithms to filter out noise and highlight the vulnerabilities that matter most.
- 📅 How often is the site updated?
- We publish updates hourly. New CVEs, emerging exploits, high-severity alerts, and major vendor advisories are continuously monitored and posted.
- 🔔 How can I stay informed about new vulnerabilities?
- You can subscribe to our newsletter, follow us on social media, or set up alerts on our platform to receive notifications about new vulnerabilities and updates.
- 💰 Is SecurityVulnerability.io free?
- Yes! Our platform is completely free to use. We believe in providing valuable resources to the Cyber Security community without any cost.
- 🛠️ Do you provide exploit details or PoCs?
- When available and publicly disclosed, we include links to proof-of-concept (PoC) exploits, or tag the vulnerability as actively exploited in the wild. However, we never host code ourselves.